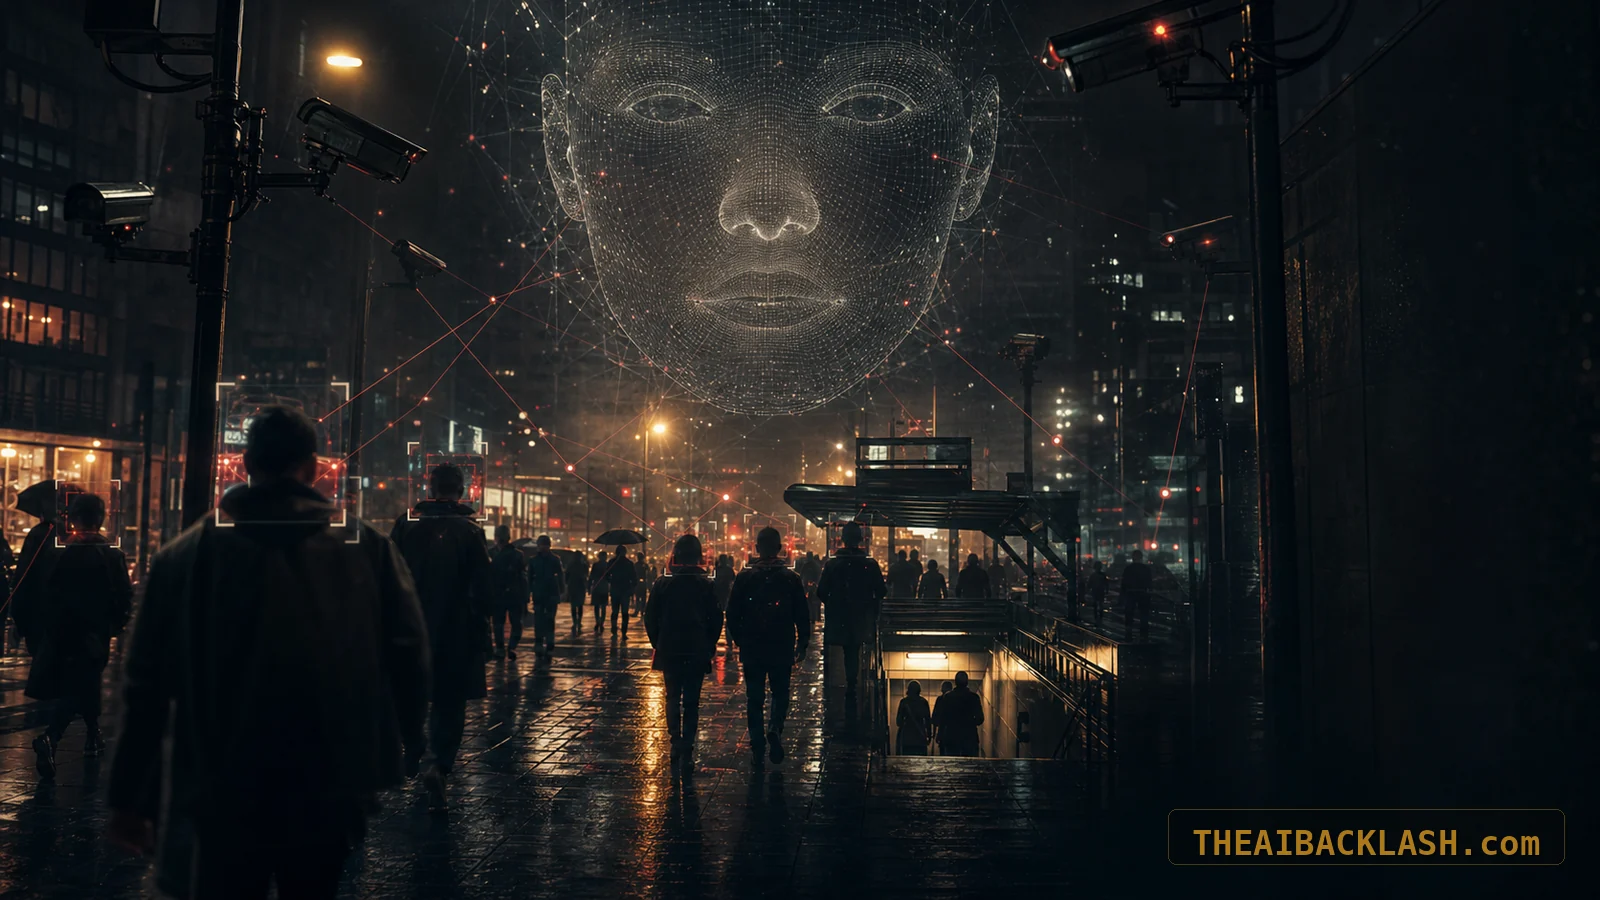
Ambient Consent Is Not Consent
Most biometric surveillance happens in spaces people must already use. The practical ability to opt out does not exist.
A sign on a wall is not consent. A paragraph in a privacy policy is not consent. A camera over a checkout lane is not consent. The language of notice and choice collapses when the monitored space is a grocery store, train station, office lobby, apartment building, hospital, school, stadium, or public street. People cannot meaningfully negotiate with the infrastructure around them.
That is the quiet trick of biometric surveillance. It moves identification out of moments where people expect scrutiny and into the background of ordinary life. You do not present an ID. You do not enter a password. You do not tap a badge. You simply walk through a space, and the system treats your body as a credential.
Defenders often describe this as convenience or safety. Faster entry. Reduced theft. Better fraud prevention. Fewer tickets. Less friction. But the removal of friction for institutions often means the removal of control for individuals. The face becomes an interface that other people own.
The New Data Broker Stack
Retail analytics, ad tech, and security vendors are converging on face and gait data as persistent identifiers. The market incentive is permanence.
The old data broker economy was built on names, addresses, cookies, device IDs, loyalty cards, location traces, purchase histories, and demographic guesses. Biometric data adds something more durable. You can clear cookies. You can replace a phone. You can use a different email. You cannot rotate your face.
That permanence is commercially seductive. A retailer wants to know whether the same person who browsed online entered a store. A landlord wants to know who entered a building. A security vendor wants to match a visitor against a watchlist. An advertiser wants to connect physical movement to digital profiles. A workplace wants to measure attendance, emotion, attention, or compliance. Each use case can be pitched as narrow. Together, they create a world where anonymity becomes suspicious.
The danger is not only one database. It is interoperability. A face template created for building access can become useful for investigations. A retail analytics system can become a loss-prevention network. A school safety tool can become a discipline tool. A phone unlock pattern can normalize biometric authentication everywhere else. Data collected for one purpose has a way of finding more profitable purposes later.
Accuracy Is Not the Only Issue
Public debate often focuses on whether facial recognition is accurate. That matters, especially because error rates have historically varied across demographic groups and because false matches can cause real harm. A bad match in a policing context can mean questioning, detention, reputational damage, or worse.
But accuracy is not the finish line. A perfectly accurate surveillance system can still be unacceptable.
If a camera identifies every person entering a reproductive health clinic, a union meeting, a mosque, a protest, a debt counseling office, or an addiction treatment center, the civil liberties problem does not disappear because the system works. In some cases, accuracy makes the system more dangerous. The more reliable identification becomes, the more chilling the monitored space becomes.
That is why biometric governance cannot be reduced to technical benchmarking. The question is not only “does it identify the right person?” The question is “should this institution be identifying people here at all?”
Watchlists Are Policy Disguised as Software
The most troubling biometric systems are often tied to watchlists. A venue, store, or agency defines a set of people to flag. The software performs the match. Security staff receive an alert. The process looks automated, but the watchlist itself is a human and institutional decision.
Who gets added? Who reviews the evidence? How long do they remain listed? Can they appeal? Are minors included? Are people listed because of arrests, convictions, accusations, debt, workplace disputes, political activity, or vague suspicion? Does the system distinguish between a person legally barred from a property and a person who merely annoyed management?
Without due process, watchlists become private punishment infrastructure. People may be denied entry, followed, questioned, or reported without ever knowing why. The system turns suspicion into an ambient condition.
The Workplace Frontier
Biometric surveillance is not limited to public streets or retail spaces. Workplaces are becoming laboratories for bodily data. Employers already use badge systems, productivity software, GPS tracking, keystroke monitoring, call analytics, and video review. Face and gait recognition fit naturally into that stack.
The pitch is operational efficiency: secure access, timekeeping, safety, compliance. The risk is behavioral control. Once identity is automated, employers may be tempted to measure presence, attention, mood, fatigue, collaboration, and deviation from expected patterns. Workers become legible not as people, but as streams of measurable conduct.
Consent is especially weak at work. An employee can technically refuse a biometric system, but refusal may mean losing hours, promotion opportunities, or the job itself. The imbalance of power makes “choice” a legal fiction.
What Should Be Off Limits
A serious biometric policy starts with bans, not dashboards. Some uses should simply be prohibited: real-time identification of people engaged in First Amendment activity, biometric monitoring in schools without extraordinary justification, emotion recognition in employment and education, private watchlists without due process, and biometric data sharing across unrelated purposes.
Where biometric systems are allowed, they should be rare, audited, time-limited, and easy to challenge. Data should be minimized, encrypted, and deleted quickly. Vendors should not be allowed to reuse biometric templates to improve unrelated products. Institutions should publish impact assessments, error data, retention rules, and appeal processes.
Most importantly, the burden should shift. Today, individuals are expected to avoid surveillance that is embedded in the environment. That is backwards. Institutions should have to prove why biometric identification is necessary, why less invasive tools are insufficient, and why the benefits outweigh the social cost.
The face is becoming a password people never chose and cannot change. Treating that as normal would be one of the great privacy failures of the AI era.
Reader Note
This article is analysis, not investment, legal, medical, or operational advice. Speculative scenarios are framed as risk arguments. Factual corrections can be sent through the published corrections process.
Topics
Related Reading
Security
Open Weights, Open Wounds
Every capability released without a control surface is a gift to whoever wants it most.
Autonomy & Control
Agents With Hands: When the Browser, Wallet, and Inbox Start Acting Without You
The scary part of agentic AI is not that it talks like a person. It is that it can click like one.
Politics & Power
The Data Center Coup: When AI Learns to Vote With Megawatts
The next power struggle may not start in a parliament. It may start at the substation.
Newer
Deepfake Democracy: The Election Interference No One Can Detect
Synthetic media is already reshaping political campaigns. Most voters will never know the difference.
Older
The Children Left Behind: AI Tutors and the Crisis of Human Connection
Schools are racing to adopt AI. But what happens when students stop learning from people?